
Transaction
7BA2C41923598C…40FD036A4F91
Block 26,285 · index 0 · indexed
Summary
- Hash
- 7BA2C41923598C8AE5344314FE180F92C05684B1E7C70398CB2940FD036A4F91
- Block
- 26,285
- Size
- 3552 bytes
- Gas used
- 8,832,884 / 10,599,520
- Fee
- 1000000ugnot
- Memo
- gnopublish
- Status
- success
Messages
- Package
- gno.land/r/moul/config/v0
Arguments · 9
- #1config
- #2README.md
- #3# `gno.land/r/moul/config/v0` _TODO: describe this package._ <!-- BEGIN GNOCONTRACTS FOOTER (generated by `make readmes`; do not edit below) --> --- Part of **[moul/gno-contracts](https://github.com/moul/gno-contracts)** — moul's versioned gno.land contracts. See the repository for the full catalog, build/test tooling, and usage. **Dependency graph:** 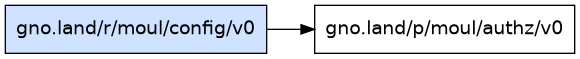 > ⚠️ **Disclaimer:** provided as-is, without warranty; not security-audited. Full disclaimer: [DISCLAIMER](https://github.com/moul/gno-contracts/blob/main/DISCLAIMER.md). <!-- END GNOCONTRACTS FOOTER -->
- #4config.gno
- #5package config import ( "errors" "gno.land/p/moul/authz/v0" ) var Authorizer *authz.Authorizer func init(cur realm) { if !cur.Previous().IsUserCall() { panic("r/moul/config must be initialized by an EOA") } Authorizer = authz.NewWithMembers(cur.Previous().Address()) } // AddManager adds a new address to the list of authorized managers. // This only works if the current authority is a MemberAuthority. // The caller must be authorized by the current authority. func AddManager(cur realm, addr address) error { memberAuth, ok := Authorizer.Authority().(*authz.MemberAuthority) if !ok { return errors.New("current authority is not a MemberAuthority, cannot add manager directly") } return memberAuth.AddMember(0, cur, addr) } // RemoveManager removes an address from the list of authorized managers. // This only works if the current authority is a MemberAuthority. // The caller must be authorized by the current authority. func RemoveManager(cur realm, addr address) error { memberAuth, ok := Authorizer.Authority().(*authz.MemberAuthority) if !ok { return errors.New("current authority is not a MemberAuthority, cannot remove manager directly") } return memberAuth.RemoveMember(0, cur, addr) } // TransferManagement transfers the authority to manage keys to a new authority. // The caller must be authorized by the current authority. func TransferManagement(cur realm, newAuthority authz.Authority) error { if newAuthority == nil { return errors.New("new authority cannot be nil") } return Authorizer.Transfer(0, cur, newAuthority) } // ListManagers returns a slice of all managed keys. func ListManagers(cur realm) []address { var keyList []address memberAuth, ok := Authorizer.Authority().(*authz.MemberAuthority) if !ok { return keyList } tree := memberAuth.Tree() if !ok || tree == nil { return keyList // Return empty list if tree is not as expected or nil } tree.Iterate("", "", func(key string, _ any) bool { keyList = append(keyList, address(key)) return false }) return keyList } func HasManager(cur realm, addr address) bool { memberAuth, ok := Authorizer.Authority().(*authz.MemberAuthority) if !ok { return false // Return false if not a MemberAuthority or doesn't exist } // Use the MemberAuthority's specific RemoveMember method, // which internally performs the authorization check. return memberAuth.Has(addr) }
- #6gnomod.toml
- #7module = "gno.land/r/moul/config/v0" gno = "0.9"
- #8/gno.MemPackageType
- #9 MPUserProd
Result log
msg:0,success:true,log:,events:[]